On-server security plugins like Wordfence are among the most common causes of degraded WordPress performance that developers overlook. This guide breaks down exactly how the problem works, how to measure it, and how to fix it without leaving your site unprotected.
Key Takeaways
Wordfence and similar on-server security plugins can dramatically inflate Time to First Byte and degrade core web vitals by executing heavy PHP logic and database queries on every single HTTP request. For wordpress site owners running WooCommerce stores, membership sites, or high traffic sites, these performance issues compound under load and directly harm search rankings.
The main bottlenecks are:
- Pre-WordPress PHP hooks loaded via auto_prepend_file that run before your wordpress website outputs any HTML
- CPU spikes from malware scanning that iterate over tens of thousands of php files, hashing and comparing against signature databases
- Bloated firewall rules evaluated in PHP on every request, competing for cpu usage with your actual application logic
- Oversized Wordfence database tables (wp_wflogs, wp_wfHits) that slow down database queries and inflate backup times across the entire site
Simply upgrading hosting or stacking another caching plugin rarely fixes the root cause because the security work still runs on the origin server. The architectural solution is an edge WAF like Atomic Edge that inspects and blocks malicious traffic before it reaches WordPress, offloading CPU and RAM while immediately improving TTFB and core web vitals metrics.
This article walks through: how Wordfence slows sites in technical detail, how to benchmark the impact, short-term mitigation settings, and how to safely migrate to edge-first security without losing protection.
The Hidden Performance Cost of WordPress Security Plugins
WordPress powers over 43% of all websites, making it a prime target for automated attacks, malware injections, and brute-force campaigns. That reality drives most wordpress site owners to install a wordpress security plugin-Wordfence, ithemes security, or the Sucuri plugin-as their first line of defense.
The problem surfaces when that defense runs inside the same PHP process responsible for rendering web pages. Picture a mid-traffic WooCommerce store: it passes most automated audits, but core web vitals scores show persistent “Needs Improvement” ratings. TTFB sits above 1 second on product and category pages. During traffic spikes-flash sales, email blasts-the server response degrades further, slow loading pages stack up, and the wordpress dashboard becomes sluggish. The culprit is not the theme or the page builder. It is the security plugin executing heavy PHP and MySQL operations on every request before a single byte of HTML is generated.
These security plugins are not inherently flawed. Their on-server architecture, however, is fundamentally at odds with modern performance expectations. Pairing a high-performance hosting provider, a content delivery network, and an edge WAF is now the preferred pattern among performance experts for combining wordpress security with speed, rather than piling heavyweight plugins on the origin.
How Wordfence Hooks Into Every Request (Where the Latency Starts)
To understand where latency originates, consider the WordPress request lifecycle. The PHP interpreter starts, loads wp-config.php, initializes the database connection, loads active plugins and themes, then begins generating HTML. Every millisecond spent before HTML output begins inflates server response time.
Wordfence’s Extended Protection mode injects a bootstrap file via the auto_prepend_file directive in the htaccess file, .user.ini, or php.ini. This causes wordfence-waf.php to execute before WordPress core, before themes, before any other plugin. The server side overhead includes:
- Initializing the Wordfence WAF engine
- Loading and evaluating firewall rules against the inbound request (URI, headers, POST body, cookies)
- Performing IP reputation lookups and rate-limit tracking
- Allocating additional PHP memory for rule processing
TTFB measures time from request to first byte received, so all of this work directly inflates it. Here is a simplified illustration of the execution order:
[PHP Start] → [auto_prepend_file: wordfence-waf.php] → [Rule evaluation]
→ [wp-config.php] → [WordPress Core] → [Plugins/Theme] → [HTML Output]
This overhead applies to all traffic: logged-out visitors, bots, API calls, AJAX endpoints, static asset requests routed through PHP, and wp-login.php requests. There is no conditional bypass for “safe” requests-every PHP-handled request pays the full initialization cost.
CPU Spikes, Malware Scans, and Real-World Slowdowns
Beyond per-request overhead, Wordfence’s malware scanning engine introduces periodic but intense server resource consumption. The scanner iterates over tens of thousands of files-core files, plugin and theme files, uploaded media-hashing contents and comparing each against a signature database. Wordfence can cause CPU spikes during malware scanning that saturate shared or VPS hosting environments.
Running comprehensive malware scans during peak traffic can exhaust server resources entirely. Wordfence can slow down sites with over 10,000 files, and most production WordPress installations contain 50,000 to 60,000 files across plugins and themes, media libraries, and backup directories. A site at that scale can experience 503 or 504 errors during full scans. Wordfence can lead to 503 errors for visitors during scans when the server cannot allocate enough CPU or I/O to handle both scanning and request serving simultaneously.
Low PHP memory limits compound the issue, often leading to site timeouts during security checks. Wordfence’s scan routines may request 256 MB or more of PHP memory, and when that collides with concurrent page generation, the process pool stalls.
The “Low Resource Scanning” option stretches the work over a longer period, but the total CPU time and disk I/O remain similar. The performance tax persists-it simply manifests as sustained moderate load instead of brief spikes, which can overlap with automated backup windows and degrade the wordpress dashboard experience for hours.
Firewall Rules, Login Security, and Per-Request Overhead
Login security, login protection, and brute-force defense are core selling points of any good security plugin. Attackers launch an estimated 2,000 brute force attacks per minute against WordPress sites, so these security features are genuinely necessary. But each firewall rule is an extra conditional check executed in PHP.
Wordfence processes its firewall rulesets by parsing each inbound request-URI path, query parameters, HTTP headers, POST body, and cookies-then running pattern matching against hundreds of rules. For high traffic sites on shared hosting, this translates directly into elevated server load. Shared hosting environments may struggle with resource-heavy Wordfence operations, especially when combined with rate limiting logic that writes IP count data to the database on every hit.
Inefficient firewall protection can lead to increased resource consumption, and this is precisely what happens when large rulesets and IP blocklists are evaluated inside PHP rather than on dedicated infrastructure. Wordfence’s firewall rules can increase server load significantly on underpowered environments.
The core issue is execution context. Running these checks at the origin PHP layer is inherently less efficient than evaluating them at the edge, on dedicated WAF infrastructure, where the origin never sees the bad traffic and server performance remains stable for legitimate visitors.
Database Bloat: Wordfence Logs and Core Web Vitals Side Effects
Wordfence maintains several custom database tables-wp_wflogs, wp_wfHits, wp_wfStatus, among others-that collect firewall events, blocked login attempts, scan metadata, and live traffic logs. Over time, these tables become a significant performance problem.
Wordfence’s database can bloat, slowing down queries across the entire site. Sustained bot traffic and attack waves cause these tables to grow into hundreds of megabytes or even multiple gigabytes, especially when cleanup jobs via wp-cron are unreliable or traffic is constant. Live Traffic Logging can cause noticeable processing lag on a website because every request triggers a database write operation.
Large security logging tables slow down operations that have nothing to do with security:
- Backup jobs must export and compress bloated tables, extending backup windows
- Admin dashboard views run queries that compete with Wordfence table locks
- Plugin update screens and WooCommerce reports experience slower response times when MySQL is I/O bound
To check the damage, developers can run this from phpMyAdmin or the command line:
SHOW TABLE STATUS LIKE 'wp_wf%';Look at the Data_length and Index_length columns. If any Wordfence table exceeds 100 MB, it is likely contributing to elevated TTFB and degraded site performance on dynamic content pages.
How to Confirm If Wordfence Is Slowing Down Your Site
Wordfence can slow down a website but may not be the sole cause of performance issues. Isolating its contribution requires a structured audit.
Step 1: Baseline measurement. Capture TTFB and full page load metrics with Wordfence enabled using WebPageTest, Lighthouse, or curl:
curl -w "TTFB: %{time_starttransfer}sn" -o /dev/null -s https://yoursite.comStep 2: Staging comparison. Clone your site to a staging site, disable Wordfence (and remove the auto_prepend_file reference), then re-run the same tests. Compare server response time differences.
Step 3: Load testing. Use tools like k6 or Artillery to simulate concurrent visitors. Monitor PHP-FPM queue depth, cpu usage, and MySQL slow query logs during the test. This reveals whether Wordfence degrades under concurrency, not just in isolation.
Step 4: Hosting metrics. Check CPU, RAM, and I/O graphs from your hosting provider during known Wordfence scan windows or heavy bot activity. Correlate resource usage spikes with response time degradation.
Step 5: Plugin profiling. Use Query Monitor, Code Profiler, or New Relic to measure per-plugin execution time. Compare Wordfence against other heavy plugins (page builders, analytics). In some user-reported cases, Wordfence consumed roughly 600 ms of execution time per request-approximately 10× more CPU resources than an average plugin.
This process ensures you are not attributing all performance issues to Wordfence when other factors may also contribute.
Core Web Vitals, TTFB, and the Security Plugin Bottleneck
Google’s core web vitals metrics include Largest Contentful Paint (LCP), Interaction to Next Paint (INP), and Cumulative Layout Shift (CLS). CLS measures visual stability of web pages during load. LCP and INP, however, depend heavily on backend performance, and TTFB is the foundational metric feeding directly into good LCP scores.
A good TTFB score is under 0.8 seconds, and Google recommends keeping TTFB under 200 milliseconds for optimal performance. TTFB impacts overall page speed and user experience. When TTFB consistently exceeds 800 milliseconds, it needs improvement-and that is exactly where many Wordfence-equipped sites land.
Even when front-end optimizations are in place-you optimize images, implement lazy loading, use a caching plugin, deliver critical css inline, and remove unused css-excessive backend processing from on-server security plugins keeps the ttfb score elevated. Core web vitals scores remain in “Needs Improvement” ranges because fast server response times are impossible when PHP is busy evaluating firewall rules before generating HTML.
Mobile devices on slower 4G networks are especially sensitive. Slow server response compounds with network latency, pushing LCP well beyond the 2.5-second threshold. Using a CDN can significantly reduce TTFB for distant visitors, but only for cached content. Dynamic content paths (cart, checkout, account pages) still hit the origin and pay the full security plugin tax.
Caching can speed up WordPress loading times by reducing server processing, but it does not cover every route. Performance experts should treat security workload as part of the overall performance budget: if firewall and login security logic run at the origin, they must be factored into every core web vitals optimization plan. Optimizing images can improve loading times and reduce CLS, but those gains are undermined when backend response takes a full second.
Short-Term: Tuning Wordfence to Reduce Performance Impact
These tweaks are mitigation steps, not a full solution. They reduce but do not eliminate the inherent on-server execution penalty. Wordfence can introduce performance overhead if left on default settings, so these adjustments are worth applying immediately.
Logging and database writes:
- Disabling Live Traffic Logging can reduce database write operations significantly. Switch to “Security Only” mode and lower retention windows to 7 days or less.
- Run manual cleanup on wp_wfHits and wp_wfStatus tables monthly. Monitor resource usage trends to catch bloat early.
Scan configuration:
- Enable “Low Resource Scanning” and schedule scans during off-peak hours to manage resource usage effectively.
- Excluding cache directories from scans can optimize performance. Also exclude large backup directories and media folders where appropriate.
- Disable scanning of images, binary files, and files outside the WordPress installation unless you have a specific reason to include them.
Firewall and feature trimming:
- Disable country blocking and rate limiting if your hosting provider or CDN already handles those functions. Duplicating these features doubles the per-request cost.
- Increasing PHP memory limits can improve Wordfence performance under load, but this is treating symptoms rather than causes.
Database maintenance:
- Regularly inspect Wordfence table sizes and truncate or optimize tables that exceed 50–100 MB.
- Consider disabling features that write heavily to the database on every request.
These changes lower the ceiling of Wordfence’s impact but do not change its architectural position in the request lifecycle.
Why Upgrading Hosting Alone Rarely Solves Wordfence Slowness
Upgrading from basic shared hosting to a managed WordPress plan can mask the overhead, but it does not remove the root cause. Per-request PHP security work still happens on every page load, every AJAX call, every API hit. A slow server becomes a slightly-less-slow server.
CPU and RAM increases buy headroom. Under sustained bot attacks or during malware scanning windows, even powerful VPS or dedicated servers experience latency spikes and degraded TTFB. Many web hosts and hosting providers now ban or discourage Wordfence’s Extended Protection on shared plans because it undermines CPU fairness for all tenants and increases infrastructure costs.
The more effective architecture separates concerns: the hosting provider focuses exclusively on PHP and MySQL performance (quality hosting for application logic), while a separate edge WAF handles login security, firewall rules, and DDoS filtering before requests ever reach the origin.
Hosting upgrades should be part of a broader strategy that includes moving heavy security operations off-server. Treating a hosting upgrade as the sole fix for plugin-induced slowness delays the inevitable performance ceiling.
Offloading Security to the Edge: How Atomic Edge Works
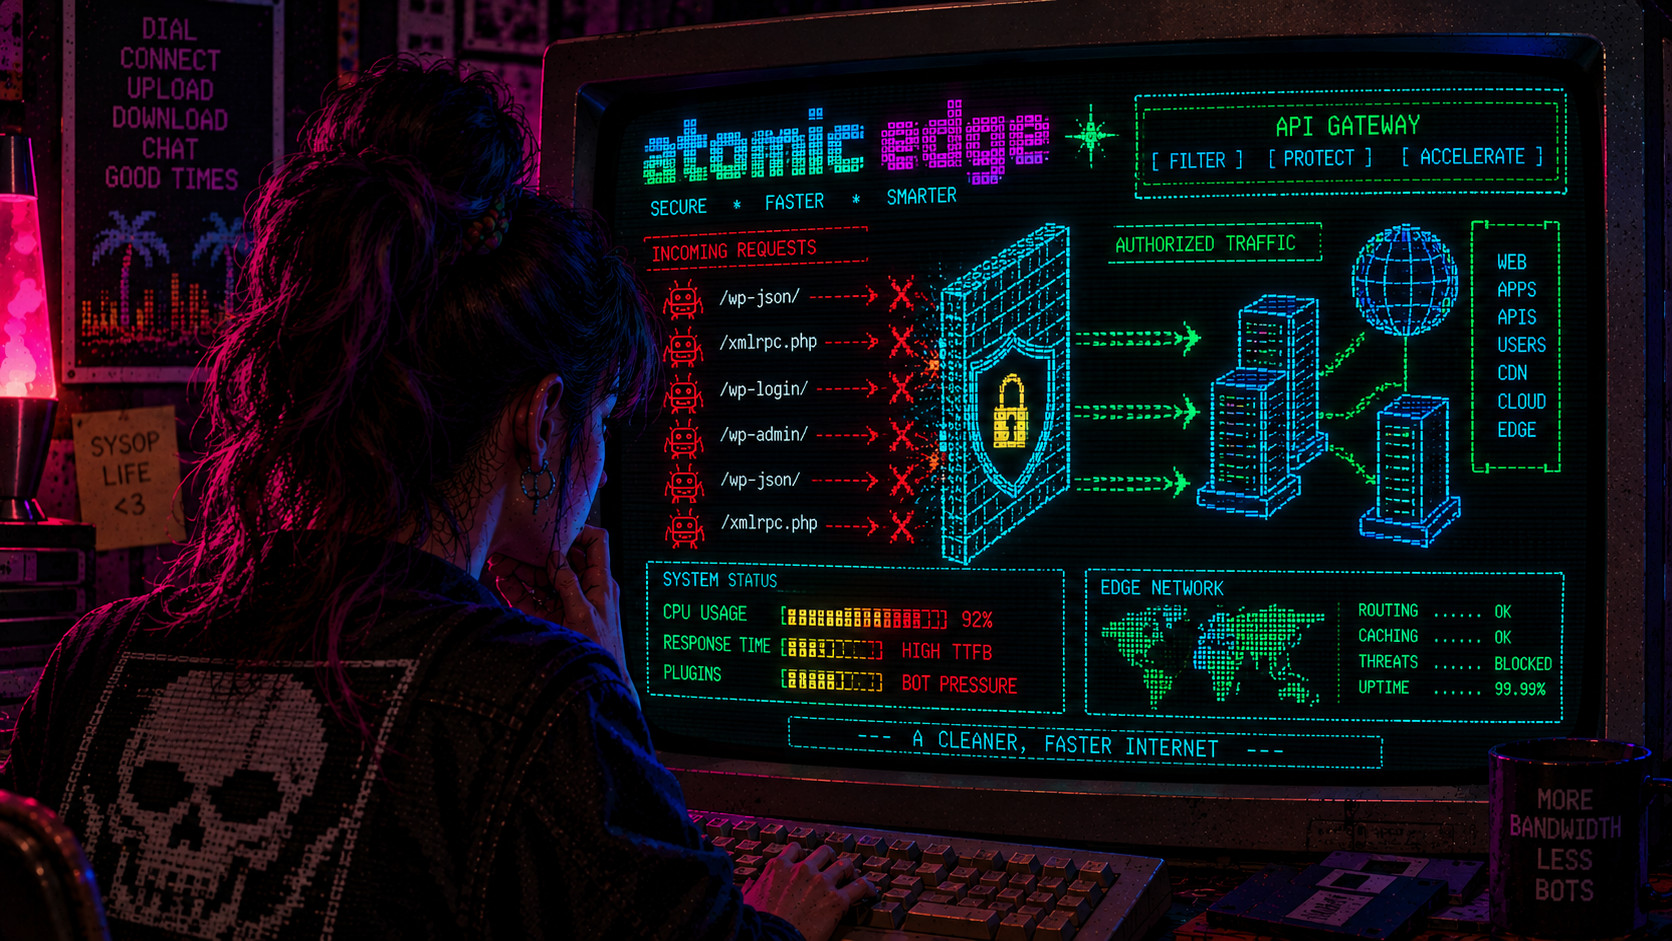
An edge WAF is a firewall and threat detection layer that runs on a globally distributed network of edge nodes, inspecting HTTPS traffic before it reaches the origin server. Atomic Edge is purpose-built for WordPress, functioning as a reverse proxy configured via DNS (A or CNAME record changes) so that all traffic flows through Atomic Edge’s edge network first.
At the edge, Atomic Edge applies:
- OWASP-aligned rulesets that catch SQL injection, XSS, and common attack patterns
- CVE-aware virtual patching that blocks exploits targeting known vulnerabilities in specific plugins and themes
- Rate limiting and brute-force protection that stops login abuse before it consumes PHP resources
- Custom firewall rules and page rules for path-level control (WooCommerce checkout, REST API, XML-RPC)
- Geo filtering to block or challenge traffic from specific regions
This architecture blocks malicious traffic at the edge, preventing it from ever consuming PHP or MySQL resources. The performance benefits are immediate: reduced origin CPU and RAM utilization, lower PHP-FPM queue depth, and improved TTFB as the server handles only legitimate, filtered traffic.
Atomic Edge logs and analytics dashboards collect blocked-request data externally, avoiding the database bloat that plagues on-server plugins. WAF logs provide full visibility into attack patterns without a single additional row written to your WordPress database.
Edge vs On-Server Plugins: A Technical Comparison
Dimension | On-Server (Wordfence, iThemes, Sucuri Plugin) | Edge WAF (Atomic Edge) |
|---|---|---|
Execution point | Inside PHP process pool, same server as WordPress | Global edge network, before origin |
CPU/RAM impact | Directly competes with application logic | Zero origin overhead for blocked traffic |
Firewall rule evaluation | PHP-based pattern matching per request | Optimized rule engines at edge nodes |
Rate limiting | Database writes per request to track IPs | Edge-level counters, no origin DB writes |
Logging | MySQL tables on origin (bloat risk) | External dashboards and logs |
DDoS resilience | Must process each request individually | Absorbs volumetric attacks at network layer |
Dynamic path protection | Adds latency to every uncached request | Filters before origin, reduces server load |
On-server plugins execute inside the same PHP process pool as your application, directly competing with WordPress and WooCommerce for CPU, memory, and database I/O. Atomic Edge processes requests on separate, optimized infrastructure. Features like one click malware removal and real-time scanning that on-server suites offer can be replaced by a combined model: Atomic Edge’s companion WordPress plugin handles malware scanning and observability with minimal footprint, while the edge WAF provides comprehensive protection against inbound threats.
This approach dramatically reduces the origin resource usage while maintaining full security coverage-without the performance penalty of a heavyweight all-in-one plugin.
Atomic Edge and Core Web Vitals: Practical Performance Gains
Moving firewall rules, rate limiting, and bot filtering to Atomic Edge reduces Time to First Byte most noticeably on uncached dynamic content pages: cart, checkout, account dashboards, and custom API endpoints. These are the pages where on-server security plugins extract the heaviest toll because caching cannot help.
The downstream effects improve core web vitals across the board:
- Lower TTFB → better LCP on both desktop and mobile devices
- Reduced CPU contention → improved INP because the server is not starved by security processing
- Stable performance during traffic bursts that would otherwise degrade visual stability and user experience
Benchmark the difference by capturing before/after core web vitals scores using PageSpeed Insights, Lighthouse, and CrUX field data after migrating. Watch for changes over the 28-day rolling window that CrUX uses for its reports.
Atomic Edge combines WAF with CDN/cache controls and page rules, so developers can serve static assets from the closest edge location while applying fine-grained security logic. Advanced features like per-path rules let you apply different security policies to /checkout/ versus /blog/, optimizing both protection and performance simultaneously.
Use the analytics dashboard to correlate blocked-request volumes with improvements in origin CPU utilization and downstream metrics. When thousands of bot requests per hour stop reaching your origin, the improvement in server performance is measurable within hours.
Migration Plan: From Wordfence to Atomic Edge Without Losing Protection
A safe migration follows this sequence:
- Set up Atomic Edge. Create an account, add your domain, and complete DNS validation. Configure baseline WAF rules, rate limits, and geo filtering.
- Monitor-only mode. Route traffic through Atomic Edge in observation mode to analyze traffic patterns and fine-tune rules before aggressive blocking. This prevents false positives on legitimate visitors.
- Parallel operation. Keep Wordfence running in a reduced state-disable the firewall component, keep malware scanning only-while verifying that edge rules correctly block common attacks (wp-login brute force, XML-RPC abuse, CVE-based exploits).
- Disable Wordfence progressively. Turn off Live Traffic Logging, disable scheduled scans, then deactivate the plugin. Remove the auto_prepend_file directive from your htaccess file, .user.ini, or php.ini. Clean up Wordfence database tables to reclaim space.
- Validate results. Re-test TTFB and core web vitals scores. Confirm that login security (2FA, IP restrictions) remains enforced via Atomic Edge rules or a lightweight dedicated plugin. Verify that your site’s security posture covers sensitive files and admin paths.
The entire DNS-based setup takes approximately two minutes. There are no PHP plugins to install on the origin for the WAF itself-protection is active as soon as DNS propagates. The companion plugin for malware scanning and inside-WordPress observability is optional and lightweight.
Best Practices for Security Without Sacrificing Speed
A layered security architecture delivers the strongest results:
- Edge WAF (Atomic Edge) for firewall rules, DDoS mitigation, rate limiting, and bot defense
- Secure hosting with proper PHP hardening, file permissions, and automatic updates
- Minimal, high-quality plugins – limit plugins to what you actually need; over 90% of breaches trace back to outdated or vulnerable plugins
- Regular updates – regularly updating wordpress core, themes, and plugins is crucial for security, and using HTTPS is essential for securing your wordpress site
For login security, enable 2FA and IP-based rate limiting at the edge rather than through a heavyweight all-in-one suite. A good security plugin should include malware scanning and login protection, but those functions can be handled by a focused, lightweight free plugin or Atomic Edge’s companion plugin rather than a full security suite that degrades every request.
To improve core web vitals alongside security:
- Use a content delivery network for static assets and lazy load images
- Apply image optimization and convert images to modern formats (WebP/AVIF)
- Remove unused css and deliver critical css inline to eliminate render-blocking resources
- Deploy server-side or edge caching for cacheable routes
Maintain observability through server logs, Atomic Edge WAF logs, and external uptime monitoring to spot security issues or unusual TTFB spikes early. The best wordpress security plugin for your stack is the one that protects without becoming a performance liability-which increasingly means keeping the heavy lifting off the origin entirely. For agencies managing multiple websites, Atomic Edge’s multi-site management eliminates the need to configure and maintain separate security plugins on each installation.
Conclusion: Reclaim Speed Without Going Unprotected
Wordfence slowing down a site is not anecdotal. Its architecture adds PHP initialization, MySQL writes, and logging overhead to every request, and this directly harms TTFB and core web vitals on modern WordPress sites. Tuning settings and upgrading hosting can mitigate symptoms, but the strategic solution is to move firewall rules, bot defense, and rate limiting to an edge WAF that handles the work before traffic reaches your origin.
Atomic Edge implements this approach with OWASP-aligned rules, DDoS mitigation, custom page rules, geo filtering, CVE-aware virtual patching, and a DNS-based setup that takes minutes rather than hours. It is designed for WordPress and handles the specific attack patterns that make this CMS a prime target.
Start by testing on a staging site or low-risk property. Measure before-and-after TTFB and core web vitals scores. Once you have validated the performance gains, roll out to production.
Atomic Edge offers a free tier to reduce server load and protect your WordPress properties without adding heavy plugins. No credit card required, no PHP overhead on your origin, and immediate visibility into the malicious traffic your server has been silently processing on every request.